Forget everything you know about digital security for a moment. Antivirus is your base-level defense, like a lock on a diary. It keeps casual snoops out. But a determined spy knows locks are only the beginning; the real work happens after they’re inside, unseen.
To counter this, you need intelligence from within your own ranks. Endpoint detection and response (EDR) delivers that insider knowledge, exposing the hidden movements of advanced attackers.
Seeing the whole picture:
EDR tools are installed on devices like laptops and servers. They do not just block threats at the gate. They watch what happens on these devices over time. It is like having a security camera in every house, recording everything. This lets you see the full story of an attack, not just its starting point.
Spotting strange behavior:
Instead of only looking for known bad software, EDR learns what normal activity looks like on your network. If a program starts acting strangely, like trying to turn off security settings, EDR notices. It flags this odd behavior, even if the program itself has never been seen as a threat before.
Connecting the dots:
A single strange event might not mean much. But EDR is great at connecting dots. It can see if one computer talks to another in a suspicious way, then tries to access sensitive files. By linking these small events, EDR uncovers the full attack plan, showing you how the intruder is moving.
Responding with speed:
Finding a threat is only half the battle. EDR lets you act fast. With a few clicks, a security team can isolate an infected computer from the rest of the network. This is like closing a door to stop a fire from spreading. It contains the problem before it can cause major damage.
Guided investigation:
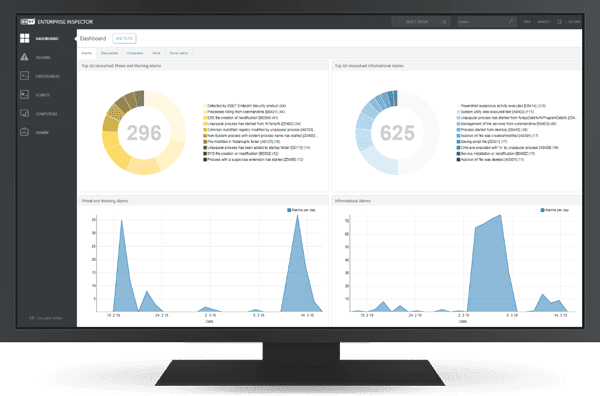
EDR provides clear guidance for your team. It does not just give a confusing alert. It offers a timeline of the attack and suggests what to do next. This helps security staff, of all experience levels, understand the issue quickly and take the right steps to fix it.
Building a stronger posture:
Using EDR over time builds a stronger defense. The system learns from every incident. It gets better at spotting new tricks that attackers use. This continuous learning makes your entire network more resilient, turning every blocked attack into a lesson for the future.